OTP Service
One-time codes are issued under a key that descends from the full chain, not a standalone secret.
Post-quantum cryptography is usually a single signature swap. DuPDF builds a hierarchy instead: two independently authenticated keys, and a family of narrow-purpose daughter keys that can only exist if both parents do.
A contract you sign today may still matter in twenty years. An adversary does not need a quantum computer now to benefit from one later — they only need to keep a copy of the ciphertext and wait.
That is why DuPDF does not treat quantum resistance as a future upgrade. The signature scheme protecting your identity, your signatures and your protected media is post-quantum on the day you install the app, and the key hierarchy is designed so that breaking any single layer is not enough.
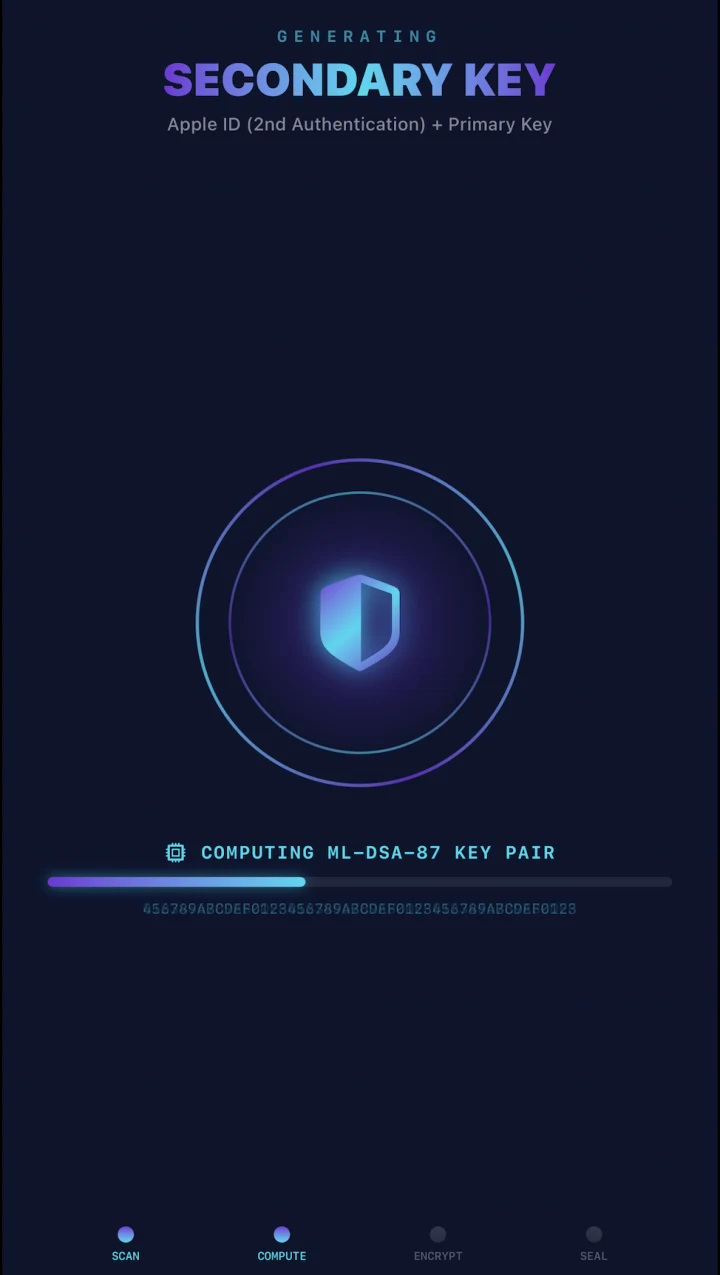
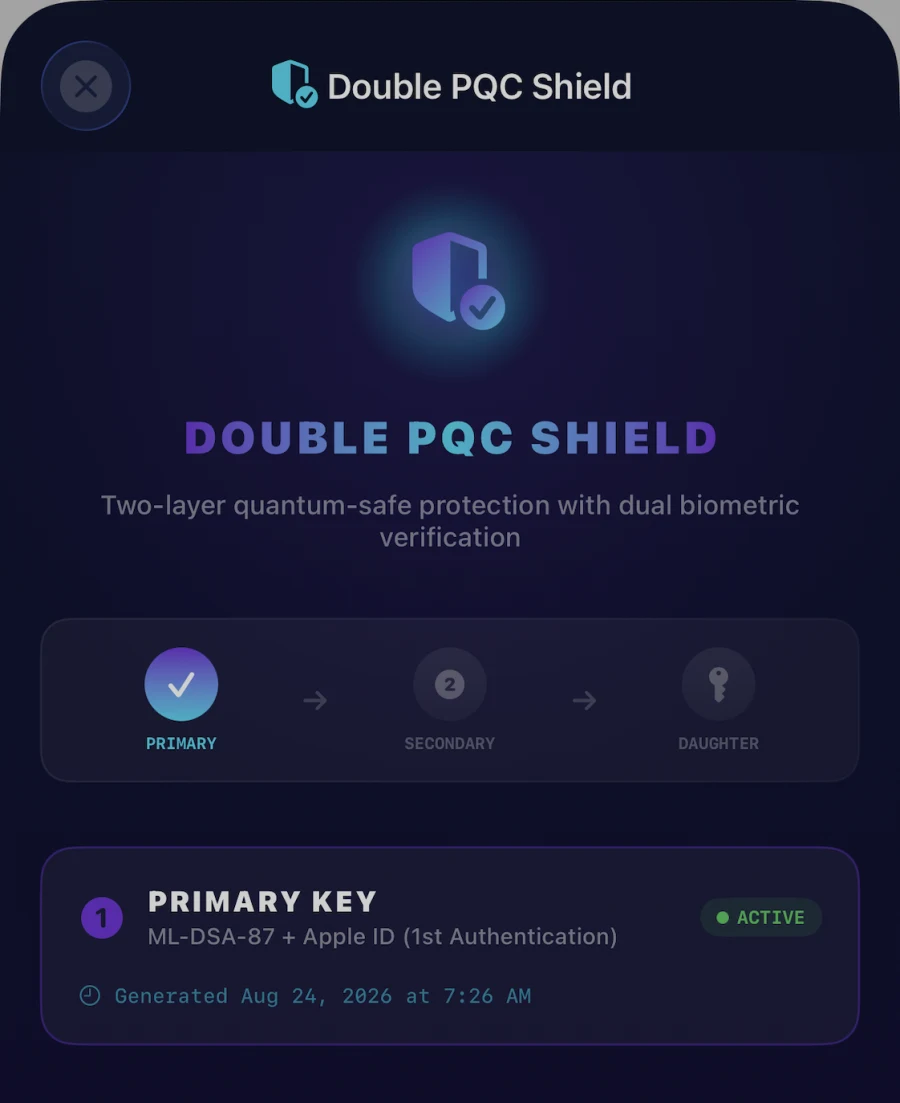
The Shield screen in the app shows this chain live, with the generation timestamp and status for every key it holds.
Primary key
ML-DSA-87 + Apple ID (1st authentication)
Generated on device during first setup.
Secondary key
Apple ID (2nd authentication) + Primary key
Cannot be produced from either input alone.
Derived daughter keys
One narrow-purpose key per protected subsystem, all derived from the secondary key.
A single stolen session, a single unlocked moment or a single leaked artifact does not produce a valid secondary key. The attacker needs the primary key and a second successful Apple ID authentication, which is bound to your biometrics.
One-time codes are issued under a key that descends from the full chain, not a standalone secret.
Integrity checks that detect a modified binary or a compromised device environment before sensitive work begins.
Your saved signatures are sealed under post-quantum protection, and signing requires you to be authenticated.
Protected media in Du-Image Studio inherits the same chain, available to Ultra Pro subscribers.
Security claims are only meaningful next to the adversary they assume. Here is ours, stated plainly.
| Adversary | Capability assumed | Design intent |
|---|---|---|
| Opportunistic attacker | Stolen or lost device, commodity hardware, offline brute force. | In scope |
| Well-resourced attacker | Large classical compute clusters and sustained targeted effort. | In scope |
| State-level supercomputer | Classical-computing attacks at essentially any scale. | In scope |
| Quantum adversary | Quantum computers at scales up to ~4.3 million physical qubits. | In scope |
These statements describe security design goals and threat-model assumptions. They are not an absolute guarantee that any system is unbreakable.
A vendor that only publishes its strengths is not telling you enough to make a decision. Protection may still be defeated, degraded or bypassed by circumstances outside DuPDF’s control.
Apple-device hardware faults, natural disasters, and compromises in hardware or software supply chains.
Security loopholes including zero-days, and intentional or unintended backdoors introduced by hardware manufacturers, component suppliers, Apple components, iOS or macOS, or third-party software vendors.
Weaknesses or backdoors involving mobile-network operators, SIMs, or SIM-service providers.
Before using DuPDF services, maintain current, independent backups of important data. To the maximum extent permitted by law, DuPDF is not responsible for data loss caused by these factors. Use genuine Apple devices and components, and choose Apple-authorized or otherwise reputable, legitimate repair and replacement services.
DuPDF does not collect, store or transmit the content of your documents, your annotations, your signatures, your drawing or text input, or any personally identifiable content you create in the app. Your files are protected by your device’s security and the app’s sandbox — which is exactly why there is nothing on our side to breach.
Documents uploaded
0
No cloud round-trip is required to edit a page.
Behavioral profiling
None
We don’t track which documents you open, edit or sign.
Data sales
Never
No sale or sharing for cross-context behavioral advertising.
Payment details
Apple
We never receive your card number or full payment details.
Generate your key chain in a couple of taps, then get on with the work.
Official download: Apple App Store only. We never email an IPA or APK, and we never send you to a third-party store.